VulnerabilityBleeping Computer
9.0 — CRITICAL
US warns of AI-powered attacks on Siemens PLCs in critical infrastructure
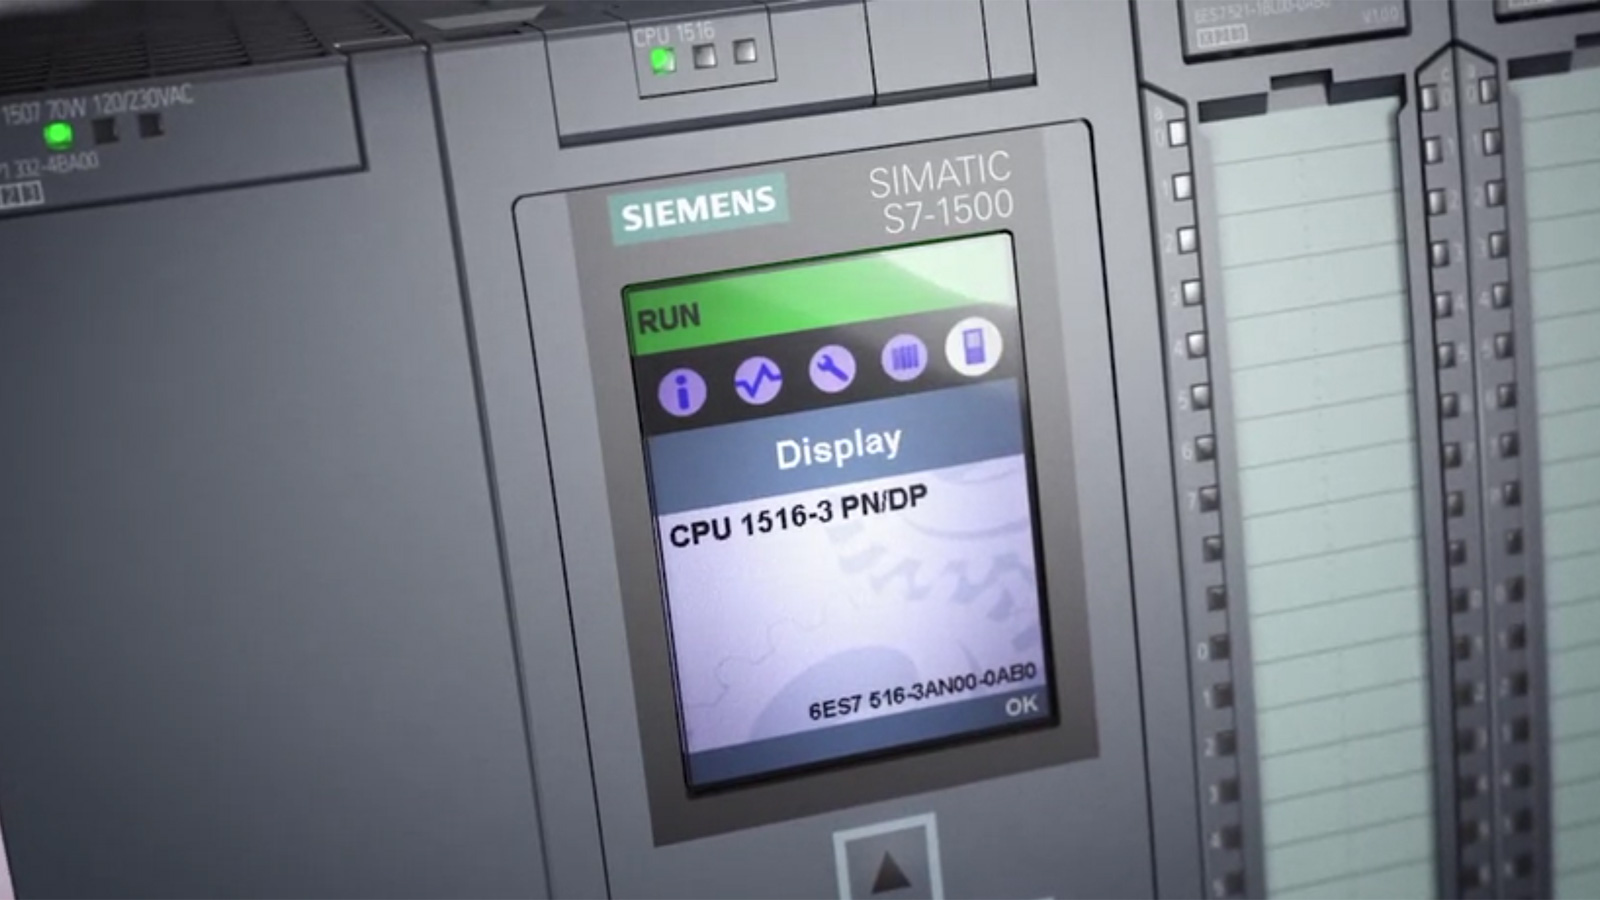
U.S. cybersecurity agencies warn that threat actors are using AI-generated scripts to exploit Siemens S7 Series programmable logic controllers (PLCs) in U.S. critical infrastructure. [...]
🤖 AI BriefingAuto-generated threat analysis
🔍Threat Overview
US cybersecurity agencies warn that threat actors are using AI-generated scripts to exploit Siemens S7 Series programmable logic controllers (PLCs) in U.S. critical infrastructure, with ongoing attacks targeting multiple sectors including Critical Manufacturing, Energy, and Water and Wastewater Systems.
⚙️Technical Details
Affected Systems
Siemens S7 Series programmable logic controllers (PLCs)CensysZoomEye
Attack Vectors
Internet scanning servicesOutdated softwareWeak authenticationS7comm protocolSnap7.dll and python-snap7 libraries
💥Impact Assessment
Severity: critical
Who Is at Risk
PLC owners and operators in Critical Manufacturing, Energy, Water and Wastewater Systems, Chemical, Food and Agriculture, and Commercial Facilities sectorsSiemens S7 PLCs used in the Defense Industrial BaseSeverity: critical
🛡️Recommended Actions
1Inventory Siemens S7 PLCs
2Install the latest security updates
3Block internet access to PLC devices
📦Affected Products
Siemens S7 Series programmable logic controllers (PLCs)Rockwell Automation/Allen-Bradley PLCs
Read the full article
This is a curated summary. The complete article is available at Bleeping Computer.