Data BreachBleeping Computer
9.8 — CRITICAL
SickKids data breach exposes employee and job applicant info
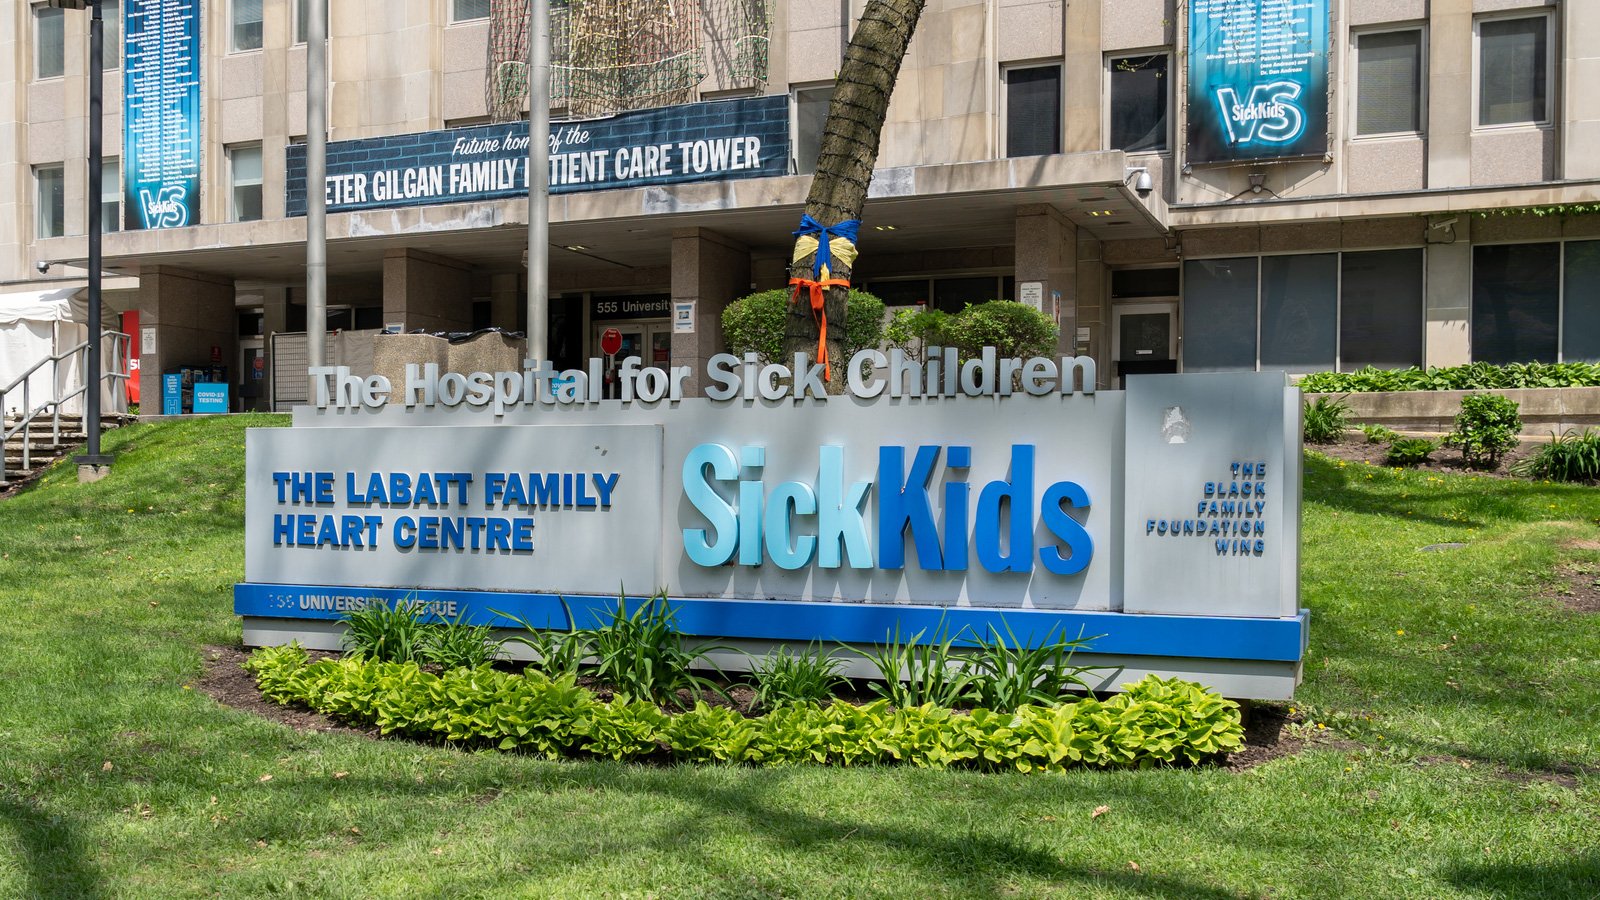
Toronto's Hospital for Sick Children (SickKids) says a cybersecurity incident exposed the personal information of some current and former employees and job applicants, stemming from a flaw in third-party software. Clinical systems and patient records were not affected. (264) [...]
🤖 AI BriefingAuto-generated threat analysis
🔍Threat Overview
A vulnerability in the MOVEit Transfer web application (CVE-2023-34362) exposed personal information of current and former employees, job applicants, and staff at a pediatric hospital, highlighting the risk of targeted attacks on healthcare organizations.
⚙️Technical Details
Affected Systems
Progress Moveit CloudProgress Moveit Transfer
Attack Vectors
NETWORK
💥Impact Assessment
Severity: CRITICAL
🛡️Recommended Actions
1Implement a patch for the MOVEit Transfer web application to prevent exploitation of CVE-2023-34362
2Monitor employee and job applicant data for potential unauthorized access
3Conduct regular security audits to identify vulnerabilities in third-party software applications
📦Affected Products
Progress Moveit CloudProgress Moveit Transfer
🔐NVD Verified DataVERIFIED
CVE-2023-34362 ↗CVSS 9.8 — CRITICAL
Attack Vector
NETWORK
Complexity
LOW
Vector String
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:HWeaknesses
CWE-89
Affected Products (CPE)
Progress Moveit CloudProgress Moveit Transfer
Read the full article
This is a curated summary. The complete article is available at Bleeping Computer.