OS SecurityBleeping Computer
8.0 — CRITICAL
Named Pipes Under Attack: Securing Windows Interprocess Communication
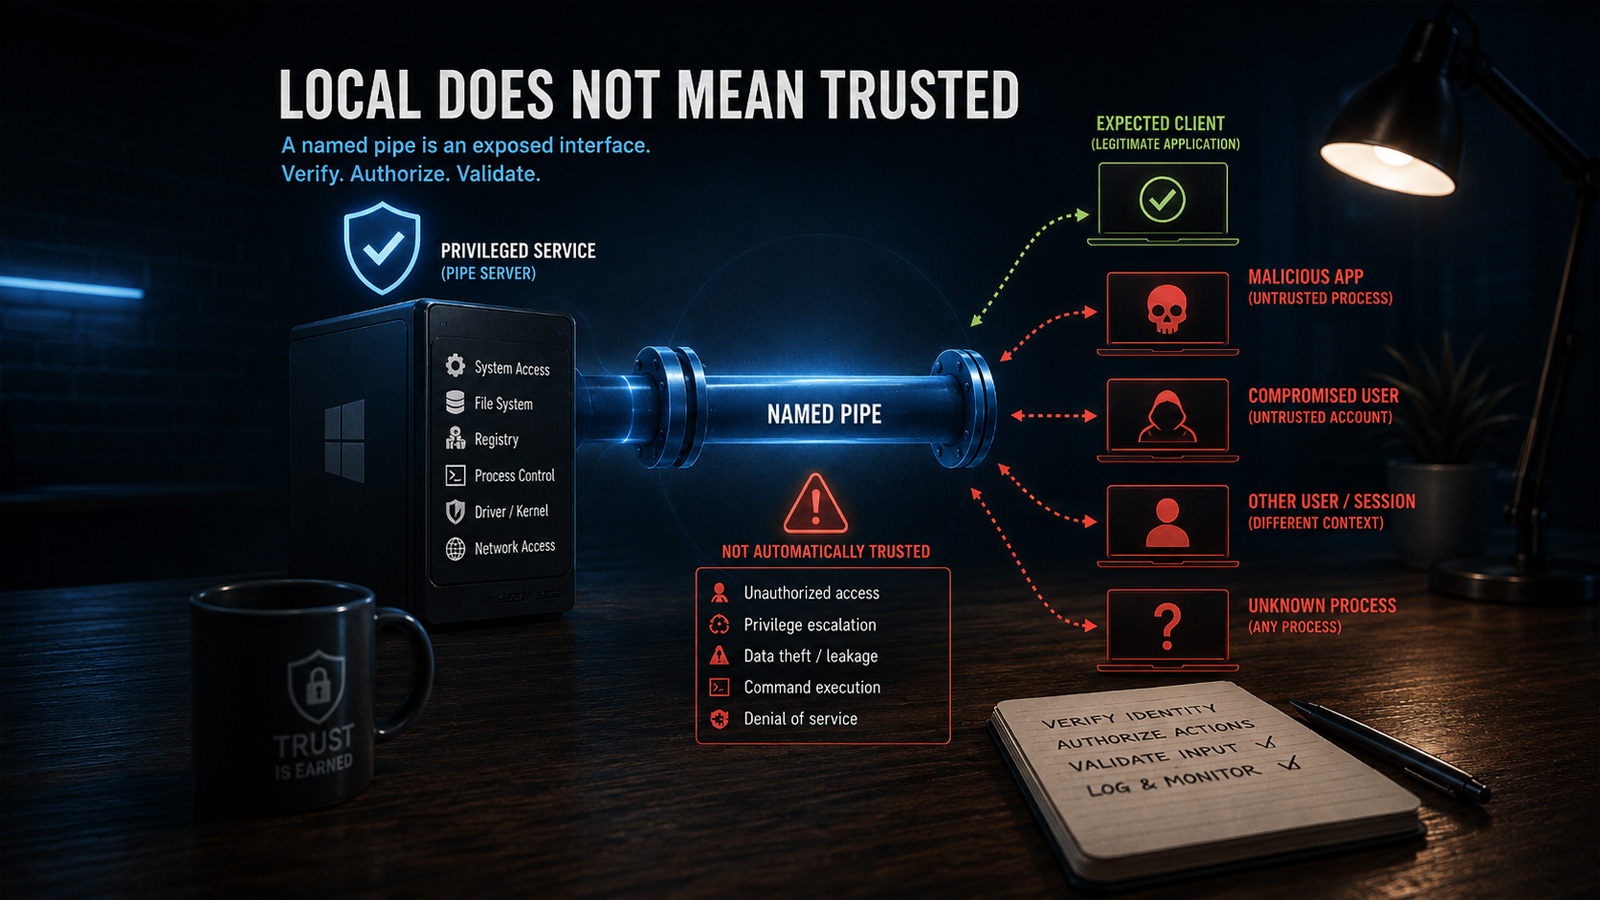
Windows named pipes provide fast interprocess communication, but weak access controls can expose privileged services to untrusted processes. ThreatLocker explains how endpoint verification, command authorization, strict input validation, and narrowly scoped privileges can help secure named-pipe communication. [...]
🤖 AI BriefingAuto-generated threat analysis
🔍Threat Overview
Named pipes are vulnerable to attacks due to inadequate access controls and verification of client and server identities, posing a risk to Windows systems with unsecured named pipe communication.
⚙️Technical Details
Affected Systems
Windows computers
Attack Vectors
Unsecured named pipe communication
💥Impact Assessment
Severity: High
Who Is at Risk
Users of Windows systems with unsecured named pipe communication
🛡️Recommended Actions
1Implement explicit and restricted permissions for named pipes
2Verify client and server identities before establishing a connection
3Use secure message framing, bounded sizes, command allowlists, schema validation, path normalization, operation-specific authorization, and safe error handling
📦Affected Products
Windows systems with named pipe communication
Read the full article
This is a curated summary. The complete article is available at Bleeping Computer.