MalwareBleeping Computer
8.0 — CRITICAL
FedRAMP Rev5 Is Ending: What the 20x Transition Really Requires
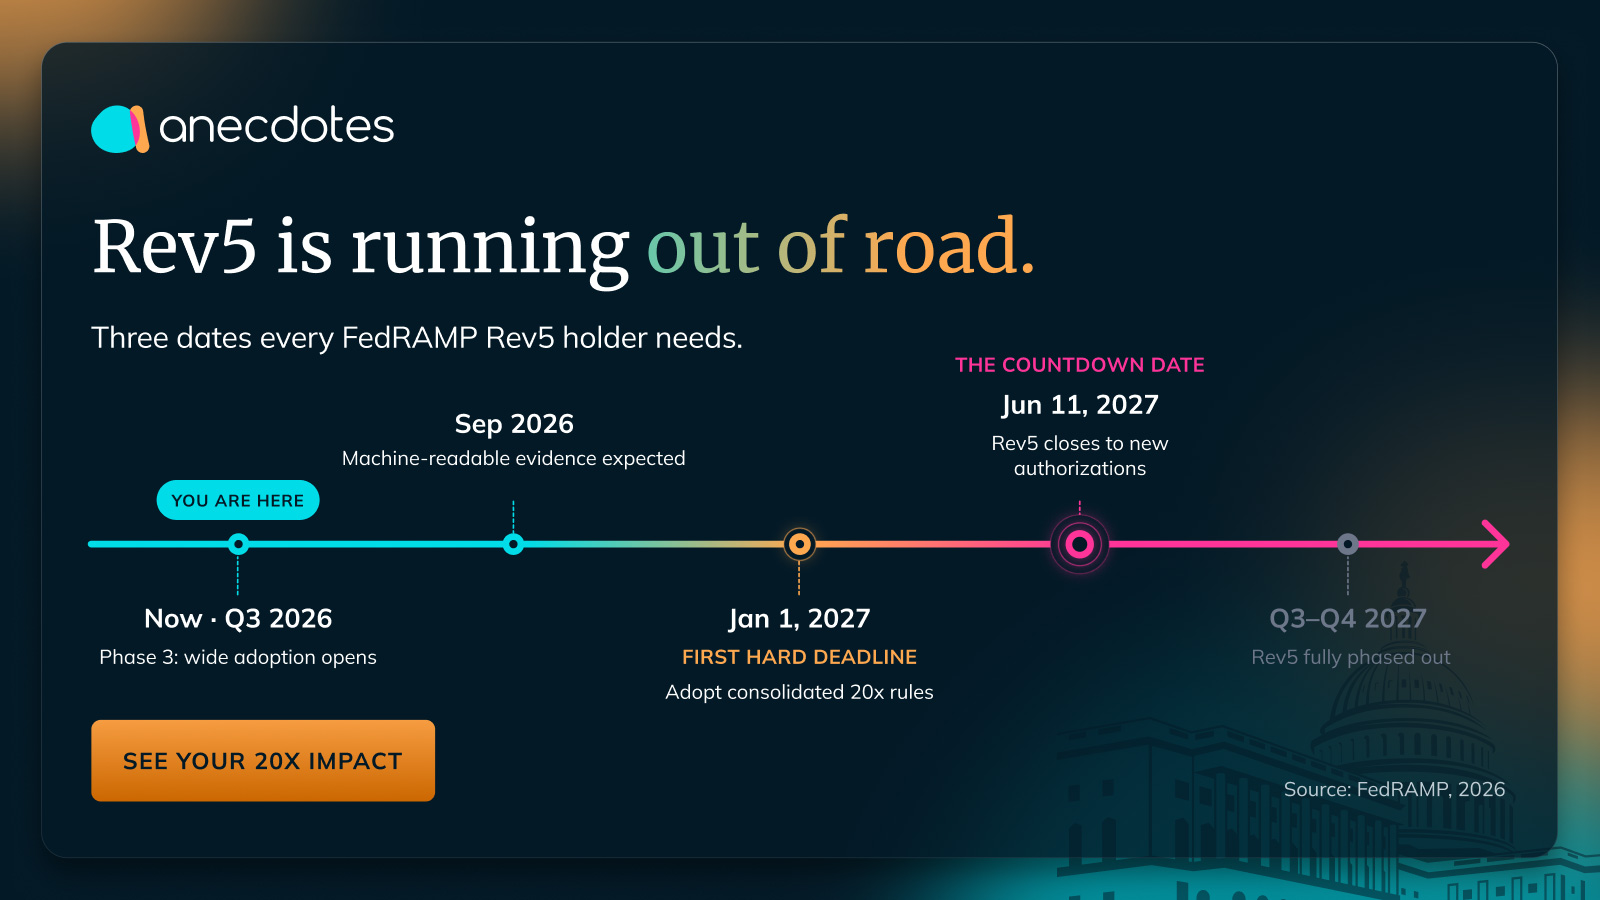
FedRAMP 20X replaces point-in-time assessments with continuous, machine-readable evidence that demonstrates security controls are working. Anecdotes explains what the transition from Rev5 to FedRAMP 20X means and how organizations can prepare for continuous, evidence-based assurance. [...]
🤖 AI BriefingAuto-generated threat analysis
🔍Threat Overview
FedRAMP Rev5 is ending and being replaced by FedRAMP 20X, which requires continuous proof of security posture through Key Security Indicators (KSIs) and machine-readable evidence.
⚙️Technical Details
Affected Systems
cloud environmentsidentitiessystems
Attack Vectors
continuous threats
💥Impact Assessment
Severity: high
Who Is at Risk
organizations using FedRAMP Rev5
🛡️Recommended Actions
1Run a KSI gap analysis to identify areas for improvement and prioritize KSIs
2Build the evidence pipeline by automating KSIs where possible and collecting machine-readable data
3Develop human-readable summaries to provide context and explain complex data to assessors
📦Affected Products
cloud platformsidentity providersSIEMsvulnerability scanners
Read the full article
This is a curated summary. The complete article is available at Bleeping Computer.