Latest IntelligencePage 87
Search by keyword →
New DOUBLECUP ClickFix service hides malware in browser cache images
A new Russian loader-as-a-service named DOUBLECUP uses ClickFix attacks to hide malicious code in PNG images cached by victims' browsers, ultimately delivering ...
Fake Roblox Xeno script launcher pushes infostealer, RAT malware
Fake Xeno Executor installers are infecting unsuspecting Roblox players with malware that provides remote access and steals sensitive information. [...]...

18 Malicious npm Packages Deliver Cross-Platform RAT to Alibaba Tool Users
Cybersecurity researchers have discovered a new set of malicious npm packages that target users of Alibaba developer tools with a cross-platform remote access t...

Malware Can Steal Your Google Synced Passkey Without Asking for Your Password or Fingerprint
New research reveals that malware already sitting on a compromised Windows PC can hijack Google’s synced passkeys and take over accounts without ever prom...
Multiple Vulnerabilities in SolarWinds Web Help Desk Could Allow for Authentication Bypass
Multiple vulnerabilities have been discovered in SolarWinds Web Help Desk, the most severe of which could allow for authentication bypass. SolarWinds Web Help D...
N-able warns of N-central auth bypass flaw exploited in attacks
N-able is warning customers that hackers are exploiting an authentication bypass vulnerability (CVE-2026-18577) affecting both hosted and on-premises N-central ...

DNA Test Software Vulnerability Allows Attackers to Alter Analysis Data
Thermo Fisher Scientific has disclosed a high-severity security flaw affecting several of its Applied Biosystems Human Identification (HID) software products, w...

Public PoC Released for Critical Rails Active Storage RCE Vulnerability
A critical vulnerability in Ruby on Rails has raised new concerns about cloud data breaches, particularly for companies that host customer platforms in Amazon W...

Google Password Manager Attacks Could Let Malware Hijack Passkey-Protected Accounts
Malware running as an ordinary user on a Windows machine can sign into a victim's passkey-protected accounts without a fingerprint, a PIN, or anything at all ap...

INC Ransomware Emerges as Dominant Actor Exploiting SonicWall SMA 1000 Flaws
The INC Ransomware operation has emerged as the "dominant threat actor" exploiting the recently disclosed security flaws in SonicWall Secure Mobile Access (SMA)...
Chinese Actor Weaponizes DeepSeek AI Agent to Attack Security Firm
Researchers intercepted and investigated the model, which was attempting to compromise more than 1,200 hosts for proxyjacking to launch further attacks....
Black Hat USA 2026 – Summary of Vendor Announcements (Part 1)
Many companies are showcasing their products and services this week at the 2026 edition of the Black Hat conference in Las Vegas. The post Black Hat USA 2026 – ...

Visa to Acquire Fraud Intelligence Firm BioCatch for $2.4 Billion
The payments giant says BioCatch’s behavioral and device intelligence will help financial institutions combat account takeovers, scams and other forms of digita...
Cyberattack Hits Liechtenstein’s Register of People Behind Companies and Foundations
The list of people behind companies, foundations and trusteeships is part of efforts to combat money laundering and terror financing. The post Cyberattack Hits ...
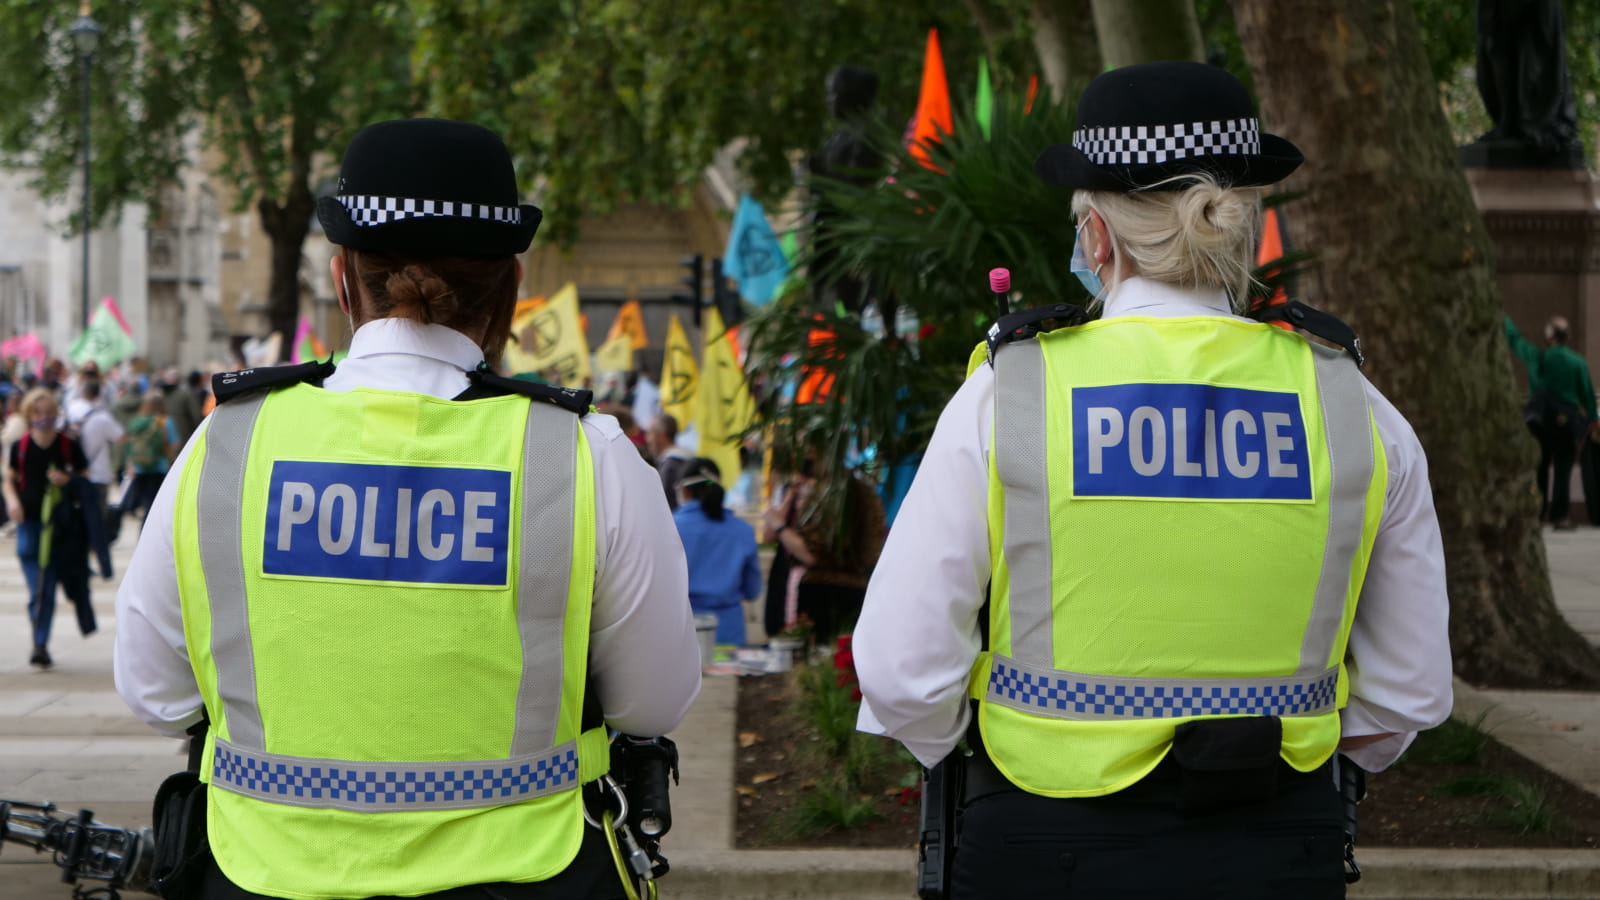
ExfilSquad hackers leak info of over 100,000 UK police officers, staff
A cyberattack on the U.K.'s Police National Legal Database (PNLD) has compromised contact data of more than 100,000 police officers and other criminal justice p...

Hugging Face Diffusers Vulnerabilities Enable Remote Code Execution Through Malicious AI Models
A set of high-severity vulnerabilities in Hugging Face’s diffusers library that allow a malicious model repository to silently execute arbitrary code on a...
Inside the Underground Business of BTMOB RAT
Flare researchers analyzed thousands of underground posts to examine how the BTMOB Android malware operation evolved into a fragmented ecosystem of resellers, s...
Inside the Underground Business of the Android BTMOB RAT malware
Flare researchers analyzed thousands of underground posts to examine how the BTMOB Android malware operation evolved into a fragmented ecosystem of resellers, s...

TP-Link TL-WR940N Vulnerability Enables Remote Code Execution Attacks
TP-Link has issued a security advisory regarding a high-severity vulnerability affecting its TL-WR940N V6 wireless router. This vulnerability, tracked as CVE-20...

Hackers Exploit VeloCloud Orchestrator Command Injection Vulnerability in the Wild
Security researchers have issued a warning about a critical command injection vulnerability that is being actively exploited in on-premises VeloCloud Orchestrat...