Latest IntelligencePage 75
Search by keyword →AI-Generated Patches Fail Half the Time
A study of more than 6,000 patches found that even working patches can introduce new bugs, break something else, or are open to bypass....

Malware Abuses Windows Hello for Business Key to Authenticate Microsoft Entra ID
A newly demonstrated technique shows how malware in a compromised Windows user session can abuse Windows Hello for Business (WHFB) cryptographic keys to authent...
Levi Strauss & Co. says hackers stole corporate data in cyberattack
Levi Strauss & Co. (Levi's) says that hackers used social engineering on three of its employees to gain access to and steal corporate data stored on their machi...

In Other News: AI Slop Limits Apple Bounties, North Carolina Port Attacks, Hackers Target Wall Street
Noteworthy stories that might have slipped under the radar: ban on Chinese data center tech, QuickFox VPN supply chain attack, IEH Corporation mailbox breached ...
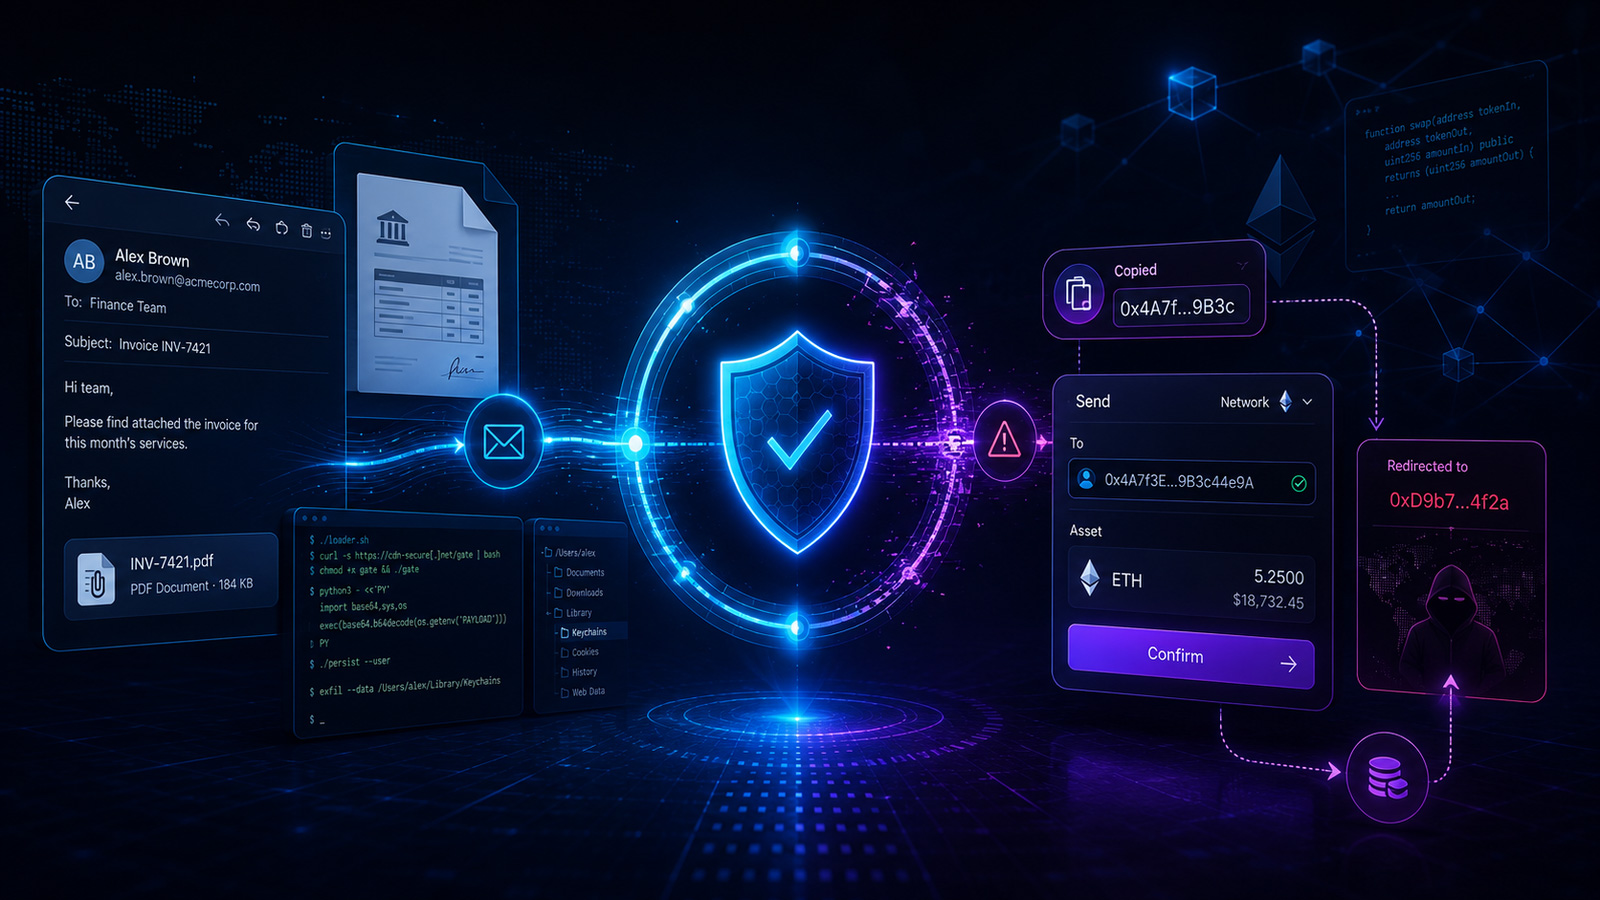
Real emails, hijacked payments: Two H1 2026 attack chains
Gen's H1 2026 Threat Report examines two separate attack chains. One used compromised business inboxes and browser manipulation in a banking-malware campaign, w...
Levi Strauss discloses data breach after social engineering attack on employees
Levi Strauss & Co. has disclosed a cybersecurity incident in which an unauthorized third party used social engineering to gain access to three employees’ co...
North Carolina Ports confirms cyberattack disrupting operations
The North Carolina Ports Authority has confirmed that a cyberattack disrupted IT systems and slowed operations at Port of Wilmington, Port of Morehead City, and...

CVE-2026-64561 Zapscape Lets KVM Guests Escape to Linux Host With Root Privileges
A Linux kernel vulnerability, tracked as CVE-2026-64561 and named Zapscape, could allow attackers to escape a KVM virtual machine and take control of its underl...

Google Chrome 151 Fixes 41 Security Flaws, Including 6 Critical Memory Bugs
Google has released Chrome 151 to the Stable channel, fixing 41 security vulnerabilities, including six critical memory-safety flaws that could enable browser c...

Hackers Breach Swiss Government SharePoint Servers, Compromise 200 Accounts
Swiss federal authorities have confirmed a cyberattack targeting SharePoint servers operated by the Federal Office for Information Technology and Telecommunicat...

New WordPress Pre-Auth XSS Could Lead to PHP Code Execution - Patch ASAP
WordPress has fixed a pre-authentication reflected cross-site scripting (XSS) flaw in its login screen that affects every version of the content management syst...

Claude in Chrome Prompt Injection Steals Gmail Codes to Hijack Slack, X, and Claude.ai Accounts
An indirect prompt injection vulnerability in Claude on Chrome can be exploited to steal email verification codes and hijack accounts on platforms like Slack, X...
IPVanish launches isolated browser to reduce Windows telemetry exposure
IPVanish has introduced a remote browser isolation feature designed to prevent Windows telemetry from directly correlating browsing activity with Microsoft̵...

Growing Up The Hard Way
Open Source had a great childhood. For two decades it got to be a kid. It ran around barefoot, gave everything away, trusted strangers, and never once thought ...
Unlimited Technology Systems data breach impacts 3.8 million people
Unlimited Technology Systems, a healthcare software and revenue cycle management provider, has suffered a data breach affecting more than 3.8 million people. Th...

Fake PDFs and Chat Apps Let Patchwork Spy on PCs and Android Phones
Patchwork, also known as Dropping Elephant, is using fake documents and chat applications to spy on computer and phone users. The long-running espionage group h...

18-Year-Old Linux SCTP Flaw Could Let Local Users Gain Root and Escape Containers
A use-after-free bug in Linux's SCTP networking code can be turned into full root on a host, and Tencent researchers say they used it to escape a container and ...

ChainDrop Worm Infects 400+ npm Packages to Steal GitHub and Cloud Credentials
ChainDrop has turned routine software installs into a route for credential theft. The self-propagating worm infected more than 400 npm packages, putting develop...
Vishing Extortion Group UNC6671 Rebrands After Making Millions
Initially calling itself BlackFile, the group has expanded operations to the Redact, Pink, Helix, and Falcon brands. The post Vishing Extortion Group UNC6671 Re...

Microsoft 365 AitM Phishing Hijacks Accounts to Collect Payroll and Finance Emails
Cybersecurity researchers have called attention to an active "widespread email-driven phishing campaign" that employs adversary-in-the-middle (AitM) techniques ...