Latest IntelligencePage 49
Search by keyword →
Virtual Event Today: CodeSecCon – Secure Your Code and Applications
CodeSecCon is the premier virtual event bringing together developers and cybersecurity professionals to revolutionize the way applications are built, secured, a...

MacSync Stealer Hides Behind 30+ Domains While Stealing Passwords and Sensitive Mac Data
MacSync Stealer is expanding the risk facing Mac users by turning everyday web browsing and Terminal activity into a route for password theft. The macOS-focused...

SilkParasite Espionage Campaign Targets Central Asian Governments with Five New RATs
A previously unreported cyber espionage operation dubbed SilkParasite has been observed targeting government bodies in Central Asia. The intrusion set makes us...

Hackers Actively Exploiting macOS’s Built-in Screen Sharing Service Vulnerability in the Wild
Hackers are actively abusing a flaw in macOS Screen Sharing to take root-level control of a small number of devices. The attacks turn a built-in remote-access f...

Windows Defender Update for 0-day Vulnerability Breaks Virus Scans
Microsoft Defender has been aborting Quick, Full, and Offline virus scans after a cluster of Security Intelligence updates reached Windows PCs on August 18, 202...

Prevalent AI Raises $22 Million to Expand Data Fabric Platform
AI-powered data fabric company Prevalent AI today announced raising $22 million in growth funding from Integrity Growth Partners (IGP). Founded in 2017 by forme...

RAVEN Tool Exfiltrates Entire Elasticsearch Databases and Maintains Access After Password Rotation
A newly detailed offensive security tool called RAVEN shows how a compromised Elasticsearch environment can become a data-loss incident with persistent access. ...
Multiple Vulnerabilities in Oracle Products Could Allow for Arbitrary Code Execution
Multiple vulnerabilities have been discovered in Oracle products, the most severe of which could allow for arbitrary code execution. Successful exploitation of ...

Hackers Compromised 14,500+ Dahua Devices Using Credential Attacks, Auth Bypasses, and P2P
Cybersecurity researchers at Hunt.io have disclosed details of a campaign that they say compromised more than 14,530 Dahua devices between June 17 and July 22, ...
US Charges 17 Iranian Hackers, Offers $10 Million Rewards for 5 of Them
The 17 members of the Mabna Institute targeted hundreds of universities and organizations in the US and abroad. The post US Charges 17 Iranian Hackers, Offers $...

Phishing 3.0: The Fight Moves to Agent Versus Agent
Most email defenses still do the job they did a decade ago. Scan the message, look for something malicious, block it. That worked when the danger sat in the pay...

StopAndProtect Uses Nearly 2,000 Hacked WordPress Sites to Spread Malware and Steal Data
Cybersecurity researchers have flagged a global cybercrime operation that abuses thousands of hacked WordPress websites as infrastructure to disseminate malware...
Microsoft fixes known issue causing Windows Defender crashes
Microsoft has resolved a bug that caused Windows Defender to crash after a recent security update, resulting in 0xc0000005 access violation errors on some affec...
Cl0p Ransomware Group Names Over 40 Victims of PTC Windchill Campaign
The cybercrime gang has listed major companies such as Shell, Philips, Fiserv, Zebra, Mindray, and Largan Precision. The post Cl0p Ransomware Group Names Over 4...

Critical macOS, SharePoint, vCenter, and Microsoft IKE Flaws Under Active Exploitation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) cat...

Oracle Releases 943 Security Patches Including Critical WebLogic Full Takeover Vulnerability
Oracle has released 943 new security patches in its August 2026 Critical Security Patch Update, addressing flaws across its enterprise software portfolio. The r...
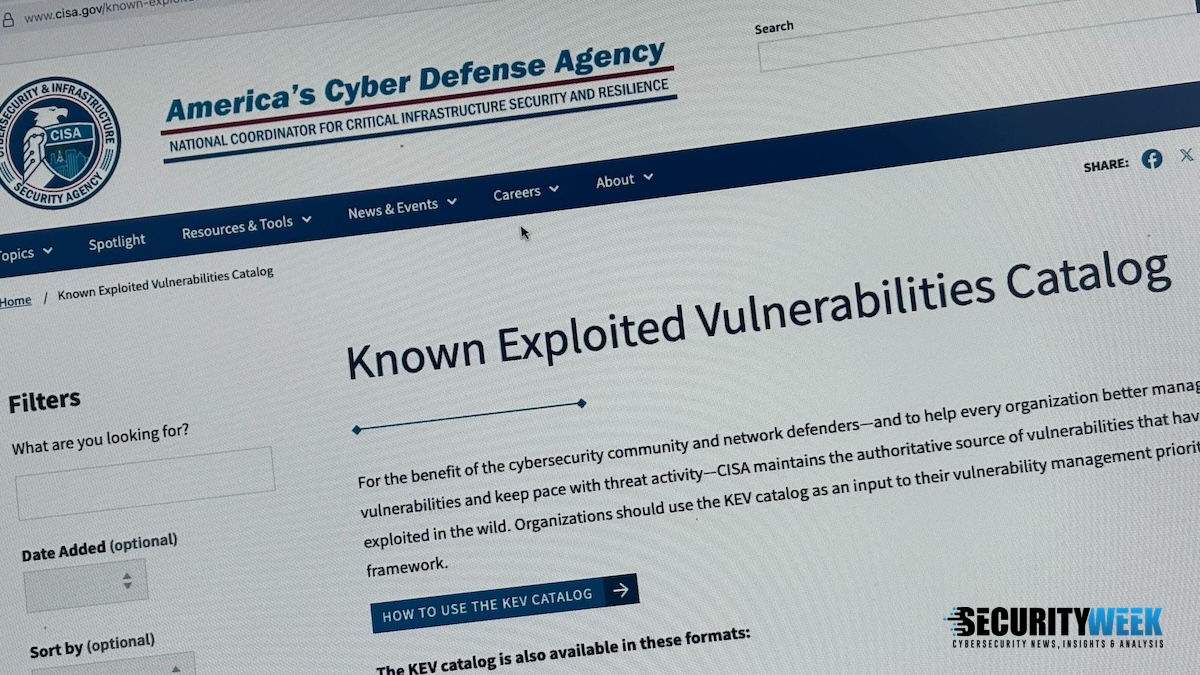
CISA Urges Immediate Patching of Exploited Microsoft, VMware, Apple Vulnerabilities
The flaws can be exploited for remote code execution, authentication bypass, and device takeover. The post CISA Urges Immediate Patching of Exploited Microsoft,...

Hackers Use Fake Claude Install Guide to Deploy MacSync Stealer and Trojanize Crypto Wallet Apps
Mac users searching for help with Claude Code are being lured into a malware campaign that turns a routine installation task into a full device compromise. The ...
Europe is creating a common security standard for VPN services
European standards body ETSI has begun the approval process for a new cybersecurity standard for VPN products, part of a wider package of 17 standards designed ...
Critical RCE flaw in Windows IKE Extension now actively exploited
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned that hackers are exploiting a critical-severity remote code execution (RCE) flaw in the ...