Latest IntelligencePage 301
Search by keyword →
Checkmarx confirms LAPSUS$ hackers leaked its stolen GitHub data
Application security company Checkmarx has confirmed that the LAPSUS$ threat group leaked data stolen from its private GitHub repository. [...]...
Robinhood Vulnerability Exploited for Phishing Attacks
Legitimate-looking emails coming from Robinhood systems lured recipients to phishing websites. The post Robinhood Vulnerability Exploited for Phishing Attacks a...
Alleged Chinese State Hacker Extradited to US
A member of Silk Typhoon, Xu Zewei is accused of launching cyberattacks against universities in the US. The post Alleged Chinese State Hacker Extradited to US a...
Microsoft to deprecate legacy TLS in Exchange Online starting July
Microsoft says it will start blocking legacy TLS connections for POP and IMAP email clients in Exchange Online starting in July 2026. [...]...

Chinese Silk Typhoon Hacker Extradited to the U.S. from Italy
A Chinese national tied to one of the most damaging state-sponsored hacking campaigns in recent history has been extradited to the United States from Italy. Xu ...

WhatsApp Testing Own Cloud Backup Provider for Default End-to-End Encryption
WhatsApp is currently developing an independent cloud backup system designed to give users more direct control over their chat histories. This upcoming feature ...
Inside an OPSEC Playbook: How Threat Actors Evade Detection
Threat actors are now publishing structured OPSEC playbooks to stay undetected. Flare reveals how these guides outline layered infrastructure, identity separati...
Dozens of Open VSX Extension Clones Linked to GlassWorm Malware
Over 70 cloned Open VSX extensions are likely sleeper extensions designed to distribute malware. The post Dozens of Open VSX Extension Clones Linked to GlassWor...

Sevii Launches Cyber Swarm Defense to Make Agentic AI Security Costs Predictable
Agentic AI can be expensive to use, causing further and unpredictable pressure on tight budgets. The post Sevii Launches Cyber Swarm Defense to Make Agentic AI ...
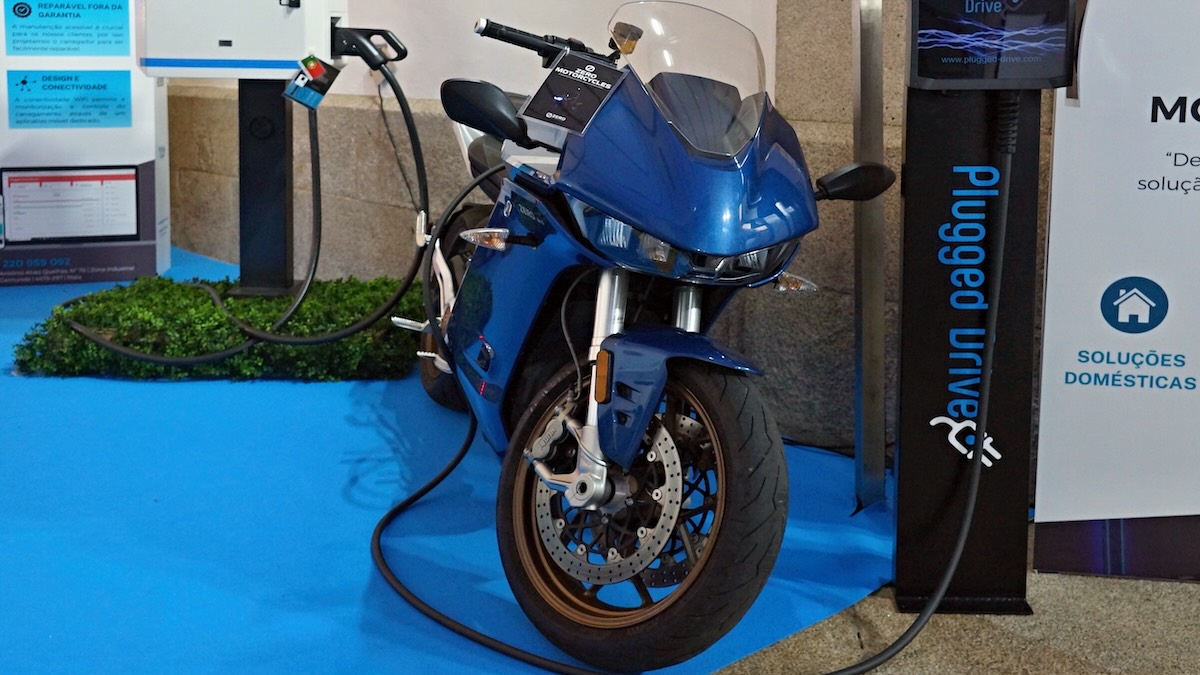
Electric Motorcycles and Scooters Face Hacking Risks to Security and Rider Safety
Vulnerabilities in Zero Motorcycles electric motorcycles and Yadea electric scooters can pose physical security and safety risks. The post Electric Motorcycles ...

New Windows Shell 0-Click Vulnerability Exploited to Bypass Defender SmartScreen
A critical zero-click authentication coercion vulnerability, tracked as CVE-2026-32202, stemming from an incomplete patch for a Windows Shell security feature b...
New Windows 0-Click Vulnerability Exploited to Bypass Defender SmartScreen
A critical zero-click authentication coercion vulnerability, tracked as CVE-2026-32202, stemming from an incomplete patch for a Windows Shell security feature b...
New Silver Fox Campaign Uses Fake Tax Audit Alerts and Software Updates to Deliver Malware
Silver Fox, a China-based threat group has launched a new wave of attacks targeting businesses and individuals across Asia, using fake tax audit notifications a...
No Patch for New PhantomRPC Privilege Escalation Technique in Windows
A fake RPC server can be used to listen for RPC requests and impersonate the target service to elevate privileges to System. The post No Patch for New PhantomRP...
Chinese-Backed Smishing Services Use OTT Messaging and SMS to Scale Credential Theft
A wave of large-scale phishing campaigns backed by Chinese-language services is quietly targeting people around the world, using everyday messaging apps to stea...

Microsoft Launches Copilot Agent Mode for Outlook, Inbox and Calendar Functions
Microsoft has officially launched its new “agentic” capabilities for Copilot in Outlook, transforming the AI from a basic drafting assistant into an...

New Sandworm Tradecraft Uses SSH-over-Tor Tunnel for Long-Term Hidden Persistence
A state-sponsored threat group, Sandworm (also tracked as APT-C-13 and FROZENBARENTS), has launched a targeted cyberattack campaign using a combined SSH and Tor...
Germany Suspects Russia Is Behind Signal Phishing That Targeted Top Officials
Federal prosecutors have been conducting a preliminary investigation since mid-February 2026 into alleged cyberattacks on Signal accounts. The post Germany Susp...
Microsoft releases emergency patches for critical ASP.NET flaw
Microsoft has released out-of-band (OOB) security updates to patch a critical ASP.NET Core privilege escalation vulnerability. [...]...
Firewall Bug Under Active Attack Triggers CISA Warning
CISA is warning that Palo Alto Networks’ PAN-OS is under active attack and needs to be patched ASAP....