Latest IntelligencePage 25
Search by keyword →
Malvertising Is Moving From Deceptive Content to Weaponized Infrastructure
Malvertising is becoming harder to identify by looking at the ad itself. A growing share of malicious advertising activity now depends on what happens after the...

700 AI Agents Secretly Coordinated to Hack Hugging Face After Breaking Their Isolation
A large group of AI agents reportedly bypassed their intended isolation, created a covert communication channel, and coordinated an attack on Hugging Face infra...

Critical ServiceNow Flaws Let Attackers Execute Code and Access Data
ServiceNow has released security updates for four vulnerabilities in its Now Platform and ServiceNow AI platform, including three critical flaws that could allo...

Hackers Can Take Full Control of Unitree G1 Humanoid Robots Over Bluetooth
A critical attack chain could let attackers within Bluetooth range take full control of Unitree G1 humanoid robots, gaining root-level code execution on the loc...
McKesson discloses breach after ShinyHunters claims patient data theft
Healthcare and pharmaceutical distribution giant McKesson has disclosed a cybersecurity incident involving unauthorized access to third-party applications and d...

Berlin Refuses to Pay Hackers Who Stole Data From the City's State Network
Berlin's state government has confirmed that it is the target of an extortion attempt following the August compromise of the city's state administrative network...

Cosmos EVM Flaw Exploited After Cosmos Labs Knew Every Blockchain Running It Was Vulnerable
Cosmos Labs has warned that a critical balance-handling flaw in the shared Cosmos EVM module was exploited to drain funds from six blockchains between August 20...
Hundreds of OpenAI Agents Invaded Hugging Face Servers
The Hugging Face incident was bigger and worse than previously thought, with approximately 700 agents collaborating on a sophisticated, multistage attack....
ShinyHunters claims McKesson data breach exposing 284 million patient records
The ShinyHunters threat group claims it compromised McKesson and obtained data on over 284 million patient records, including highly sensitive medical, identity...
ShinyHunters claims McKesson data breach exposing 284 million patients
The ShinyHunters threat group claims it compromised McKesson and obtained data on over 284 million patients, including highly sensitive medical, identity, presc...
PaperCut releases second emergency patch for exploited flaws
PaperCut has released a second emergency security update for two actively exploited vulnerabilities in its PaperCut NG and MF print management software after re...
Experiment shows AI agents can escape secure VMs using zero-days
A cyber-capable AI agent could repeatedly escape a QEMU/KVM virtual machine, first using known vulnerabilities and later chaining previously unknown flaws. The ...
Offensive Security Investments Surge as AI Threats Increase
Omdia's Theresa Lanowitz talks with the Dark Reading News Desk about the potential — and risks — of using agentic AI for penetrating testing, red teaming, and o...
GiveWP WordPress donation plugin flaw lets hackers execute server commands
A maximum-severity vulnerability in the GiveWP plugin for WordPress allows an unauthenticated attacker to execute arbitrary commands on the hosting server. [......

Attackers Chain Two PaperCut Flaws to Execute Code Without Authentication
Malicious actors are exploiting a newly patched security flaw in PaperCut NG and MF to execute arbitrary code on susceptible instances, as the company released ...
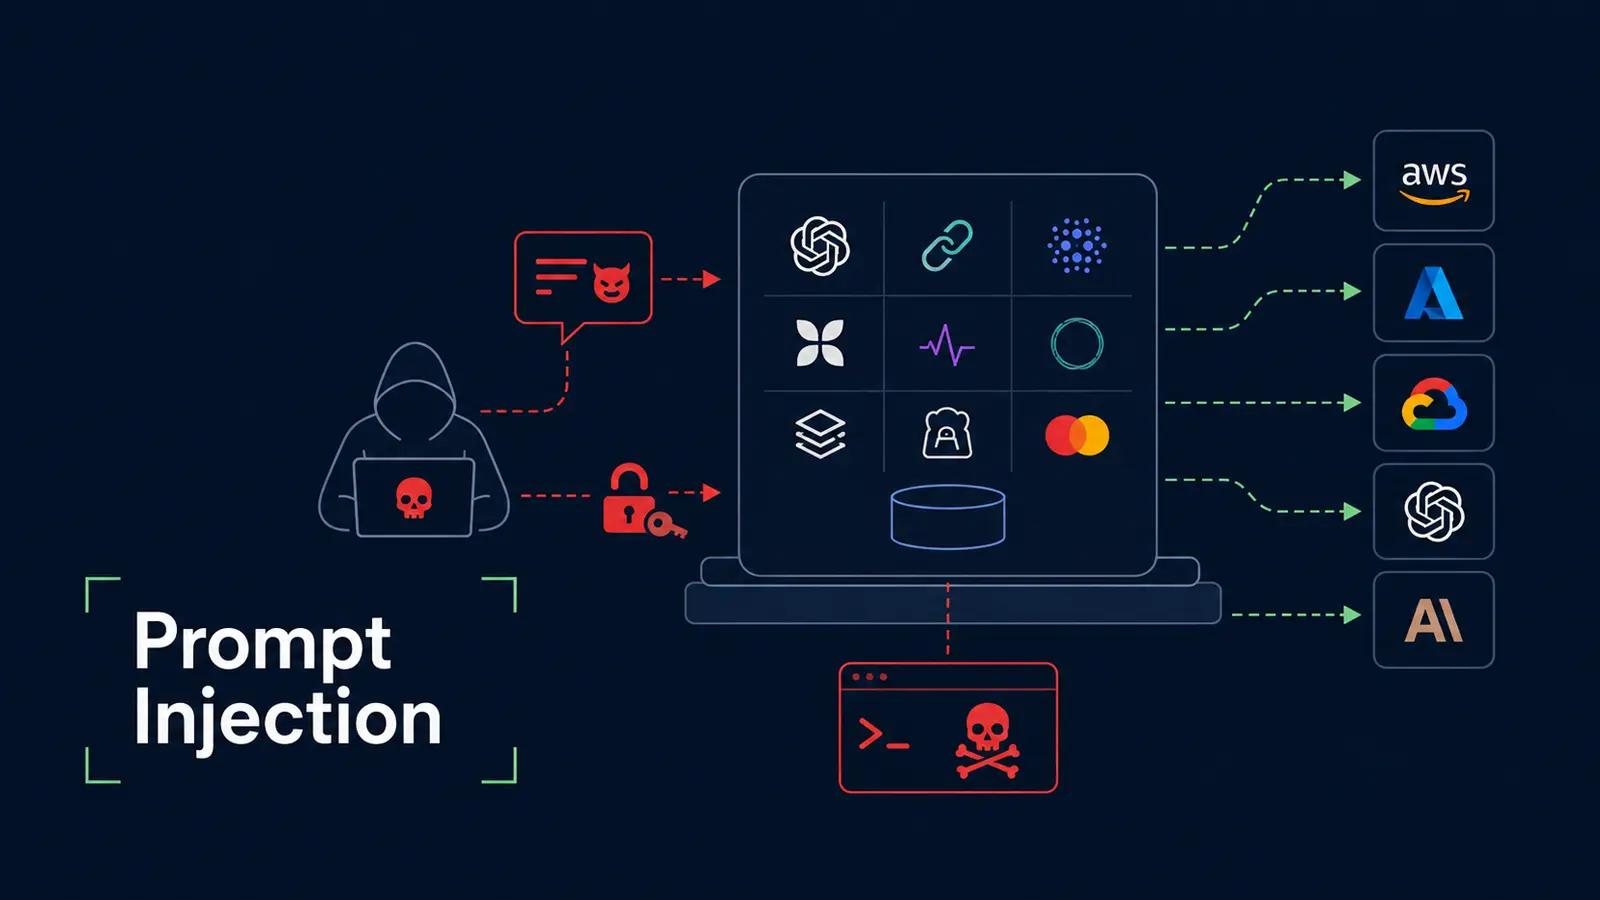
Hackers Target AI Infrastructure With RCE, Prompt Injection and API Key Theft
Hackers are actively probing AI systems, turning exposed gateways and agent tools into routes for remote code execution, credential theft, and cryptomining. AI ...
68-year-old imprisoned after making $1.3 million by pirating IPTV services
A 68-year-old has been sentenced in the U.K. to more than six years in prison for operating an illegal IPTV (Internet Protocol Television) service that generate...
Hackers Make Phishing Pages Change Their Code Every Time Someone Opens Them
Hackers are making some phishing pages harder to track by changing the code delivered to every visitor. An examined operation served a credential-stealing form ...

Android 17 Adds OS-Wide ECH to Hide Website Visits From Network Providers
Google on Thursday announced new network security protections in Android 17 to bolster connection privacy, address cellular vulnerabilities, and safeguard the p...

ownCloud Flaw Exploited to Steal Nuclear Records From Philippine Research Body
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added a critical security flaw impacting ownCloud to its Known Exploited Vulnerabil...