Latest IntelligencePage 242
Search by keyword →AI-Assisted Exploit Development Outpaces Scanner Detection
Attackers are using AI to dramatically reduce the time they need to develop a working exploit for a CVE, according to new research....

Grandoreiro Malware and BTMOB RAT Campaigns Target Windows and Android Users
Latin America and Europe become the target of two banking trojan campaigns that are designed to infect Windows and Android devices with Grandoreiro and BTMOB ma...

Malicious npm Package Stole Files From Claude AI User Directory via GitHub
Cybersecurity researchers have discovered a new malicious package on the npm registry that comes with information stealing capabilities. According to OX Securi...

Motorola Phones Preinstalled App Found Hijacking Amazon App to Inject Affiliate Codes
A hidden system application bundled with Motorola smartphones has been caught intercepting user-initiated Amazon app launches and silently redirecting them thro...

Attackers Can Exploit BadHost to Access Sensitive AI Agent Server Endpoints
A newly disclosed critical vulnerability, tracked as CVE-2026-48710 and dubbed “BadHost,” is putting thousands of AI-powered applications at risk by enabling au...

New BTMOB Malware Lets Attackers Remotely Control Android Devices
New Android malware dubbed BTMOB is arming even low-skilled attackers with full remote control over infected phones by combining a powerful RAT engine with a no...

CISA Warns of LiteSpeed cPanel Plugin Vulnerability Exploited in Attacks
CISA has issued an urgent warning regarding a critical vulnerability in the LiteSpeed cPanel Plugin, identified as CVE-2026-48172, which is currently being expl...

GitHub Enterprise Server 3.20.3 Released With Fox for Critical Vulnerabilities
GitHub has shipped GitHub Enterprise Server (GHES) 3.20.3 as a security‑driven patch release that fixes multiple critical and high‑severity vulnerabilities and ...

Windows Kernel Vulnerability Allows Attackers to Modify Kernel Memory Counters
A critical Windows kernel vulnerability, tracked as CVE-2026-40369, has been disclosed, enabling attackers to achieve full SYSTEM-level privilege escalation eve...
Vulnerability in Popular Conference Software Granted Attackers a 100% Talk Acceptance Rate
Novee researchers discovered an account takeover vulnerability in the open source CFP management tool Pretalx. The post Vulnerability in Popular Conference Soft...
Can you enforce strong Active Directory password rules without frustrating users?
Strong Active Directory passwords don't have to come at the expense of usability. Specops Software explains how passphrases, breached password protection, and s...
Glassworm botnet disrupted after resilient C2 infrastructure takedown
The Glassworm botnet targeting developers in software supply-chain attacks has been disrupted after researchers took down its resilient command-and-control infr...

Link11 is fully committed to Europe and is opening a Customer Excellence Hub in Lisbon
Frankfurt am Main, Germany, May 27th, 2026, CyberNewswire Link11, a European provider of cloud-based IT security solutions specializing in network and web appli...
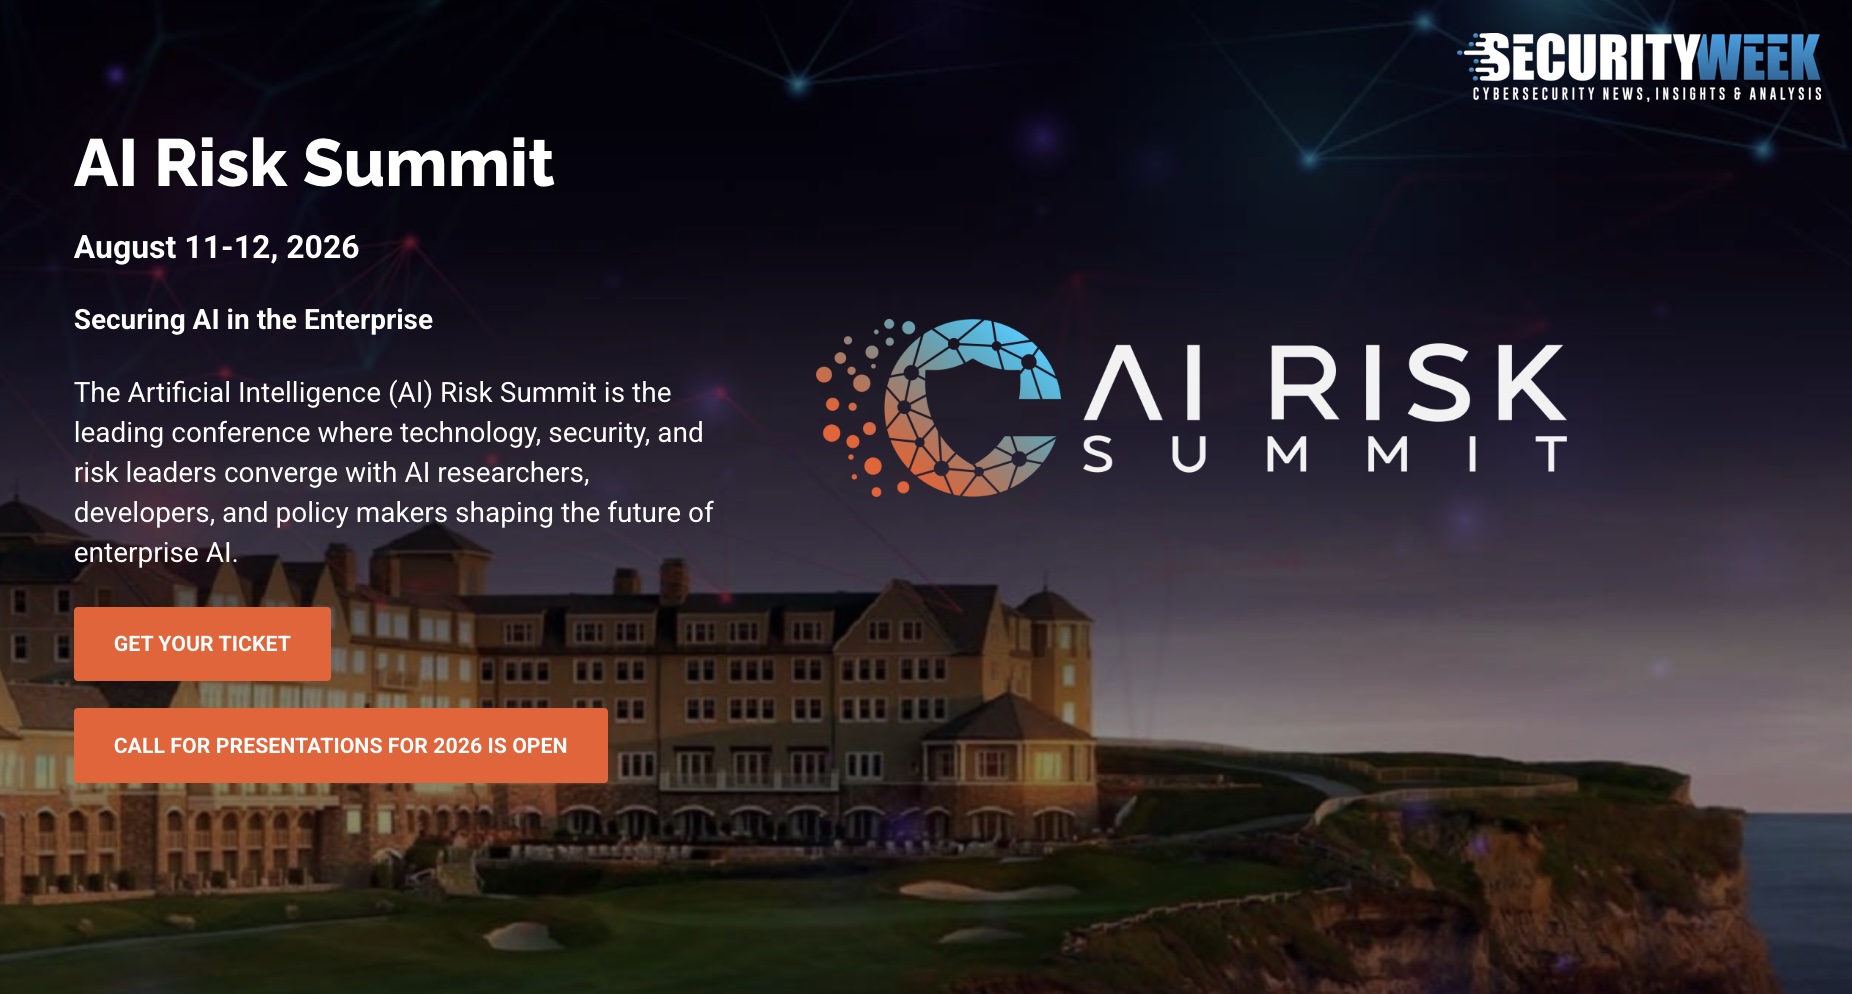
SecurityWeek to Host AI Risk Summit August 11-12 at the Ritz-Carlton, Half Moon Bay
Now in its third year, the AI Risk Summit is the leading conference that brings together CISOs, security leaders, AI researchers, developers, policymakers, and ...

Seedworm APT Abuses Signed Fortemedia and SentinelOne Binaries for DLL Sideloading
A well-known Iran-linked hacking group has been caught running a far-reaching espionage campaign that touched at least nine organizations across nine countries ...
Cybersecurity Evolution: How We Went From Perimeter Defense to AI-Native Security
The cybersecurity industry of 2006 barely resembled today's billion-dollar behemoth. As part of Dark Reading's 20th anniversary celebration, we trace the indust...

RevEng.AI Raises $15 Million to Hunt for Flaws and Backdoors in Software Binaries
Using an AI model called BinNet, RevEng hunts vulnerabilities and backdoors in released software binaries. The post RevEng.AI Raises $15 Million to Hunt for Fla...
FBI warns of in-person data theft attacks from extortion gang
The FBI warned on Tuesday that the Silent Ransom Group (SRG) extortion gang is now targeting U.S.-based law firms in in-person data theft attacks. [...]...

GlassWorm Malware Takedown Disrupts Developer Supply Chain Attack Infrastructure
CrowdStrike, in partnership with Google and the Shadowserver Foundation, has announced the simultaneous disruption of all command-and-control (C2) channels asso...

3 SOC Steps that Shut Down Incident Risks Early
Most organizations still picture cyber defense as a fortress problem: build stronger walls, add more guards, buy another detection engine. But modern incidents ...