Latest IntelligencePage 111
Search by keyword →
Malicious RubyGems Turn Developer Machines Into Monero Miners and Spread Through SSH
A malicious RubyGems campaign has turned seemingly useful developer packages into tools for hidden cryptocurrency mining. The poisoned packages can consume a ma...
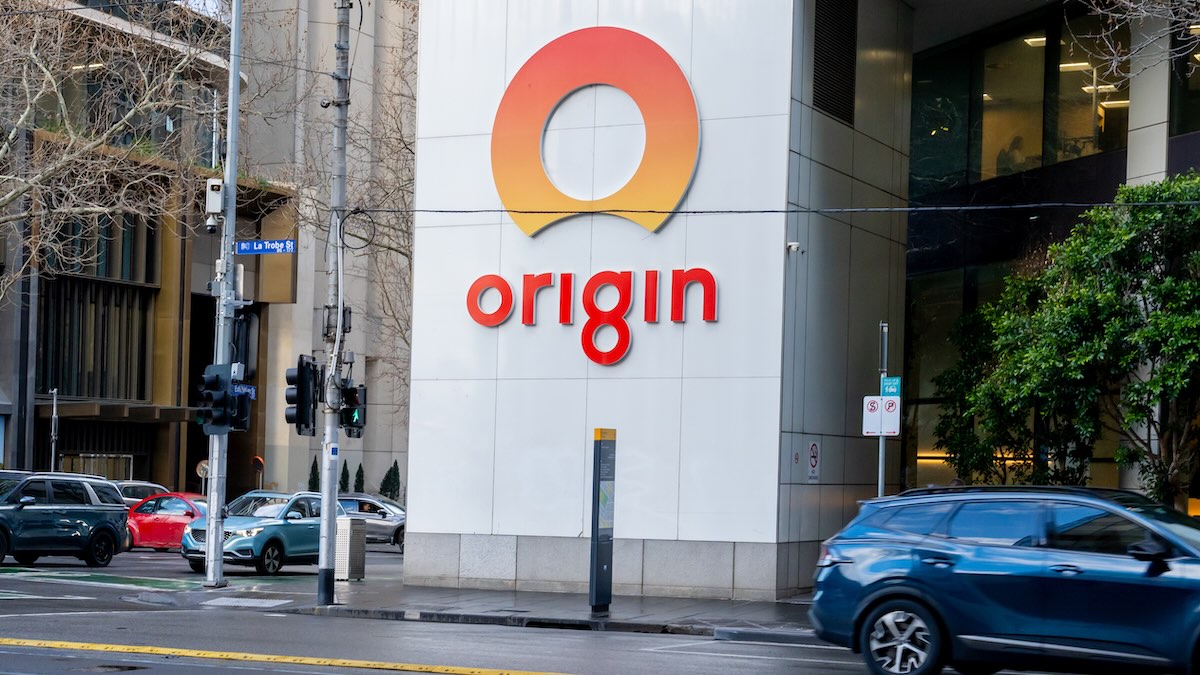
Data Breach Confirmed After Australian Energy Giant Origin Is Hacked
A hacker claims to have stolen the information of 2 million Origin Energy customers and is threatening to leak it. The post Data Breach Confirmed After Austral...

Microsoft 365 Services Outage Impacted Teams, Copilot, Purview and Other Services
A Microsoft 365 outage disrupted access to several widely used enterprise services, including Microsoft Teams, SharePoint Online, OneDrive, Copilot Chat, Micros...

Hackers Allegedly Claim Breach of Decathlon Customer Database With 160 Million Records
A threat actor is allegedly claiming to possess and sell a Decathlon customer database containing approximately 160 million records. The database was advertised...
Russian Hackers Exploit Zimbra Zero-Day Against US, Ukraine Targets
A state-sponsored threat group, dubbed "Laundry Bear," sends "half-click" phishing emails that require a victim only to open or preview the message....
New Dolphin X malware uses AI to rank high-value targets
A new Dolphin X remote access trojan claims to use an AI-powered profiling feature to score and rank infected users, helping cybercriminals identify which victi...
Australian energy provider Origin says data breach exposes client data
Origin Energy has confirmed that an unauthorized party accessed and subsequently leaked customer data online, exposing sensitive personally identifiable informa...
Fake Claude app promoted by Bing ads pushes SectopRAT malware
A malvertising campaign on the Bing search service is pushing a fake Claude desktop app installer hosted on a legitimate Claude.ai domain to deliver the SectopR...

Russian Espionage Group Exploited Zimbra Zero-Day to Steal Mail and 2FA Codes
A Russian state-supported espionage group spent months reading Western mailboxes through a then-unknown flaw in Zimbra's webmail client. The payload goes after...

Hackers Abuse Notepad++ Plugins to Compromise Your System Silently
A stealthy new campaign in which the UAC-0099 threat cluster hijacks a legitimate Notepad++ plugin to quietly plant malware on victim machines, marking a signif...
macOS flaw lets malware replace trusted apps without security warnings
Security researchers Talal Haj Bakry and Tommy Mysk have disclosed a macOS weakness that allows malware already running under a user's account to silently repla...
Russian hackers exploit Zimbra zero-click flaw for email theft
CISA is warning that the Russian state-sponsored hacking group Laundry Bear, also known as Void Blizzard, is targeting organizations using Zimbra Collaboration ...
Hackers abuse Notepad++ plugins to stealthily install malware
Ukraine's CERT has uncovered attacks distributing an archive containing the legitimate Notepad++ application and a malicious utility called LunchPoke disguised ...

Chaos Ransomware Turns Your Chrome and Edge Web Browser Into an Invisible Malware Command Channel
Chaos ransomware has introduced a new way to hide attacker activity inside everyday web browsing. The group’s msaRAT remote-access tool turns Chrome or Microsof...
Microsoft 365 outage affects Teams, SharePoint and other services
Microsoft Teams and several Microsoft 365 services are experiencing an ongoing outage, with users reporting problems accessing Teams, SharePoint, Excel and the ...

Hackers’ OPSEC Mistake Exposed a Global Espionage Campaign and Its New TriBack Malware
A simple mistake by cyber spies has pulled back the curtain on a wide ranging espionage effort. It reached hospitals, government offices, and schools across sev...

OpenAI Fixes ChatGPT Agent Flaw That Could Let Attackers Forge an AI Insider
AgentForger allows an attacker to create, insert and remotely control an invisible autonomous AI agent inside a victim organization. The post OpenAI Fixes ChatG...

ThreatsDay: Android Spyware, PLC Attacks, AI Image Prompt Injection + 12 More Stories
Most of this week's trouble came dressed as something useful. A package stole data. A fake extension opened remote access. A safety app became spyware. An imag...
Is Patching Dead? Vulnerability Management in the Post-Mythos Era
You cannot out-patch a machine that writes a working exploit from a vulnerability description in twenty hours. Stop trying to optimize a game you cannot win. Th...
Chick-fil-A Accounts Get Fried in Credential Stuffing Attack
Threat actors used credentials obtained from other companies to hack into Chick-fil-A One accounts. The post Chick-fil-A Accounts Get Fried in Credential Stuffi...