Latest IntelligenceMalwarePage 8
Search by keyword →
Microsoft warns of surge in ACR Stealer attacks on customers
Microsoft has observed a surge in attacks using the ACR Stealer malware to steal browser-stored passwords, authentication tokens, and sensitive documents from i...

Coca-Cola discloses ransomware attack disrupting fairlife production in the US
The Coca-Cola Company has disclosed that a ransomware attack affecting its wholly owned dairy subsidiary, fairlife, has temporarily halted fairlife's US product...
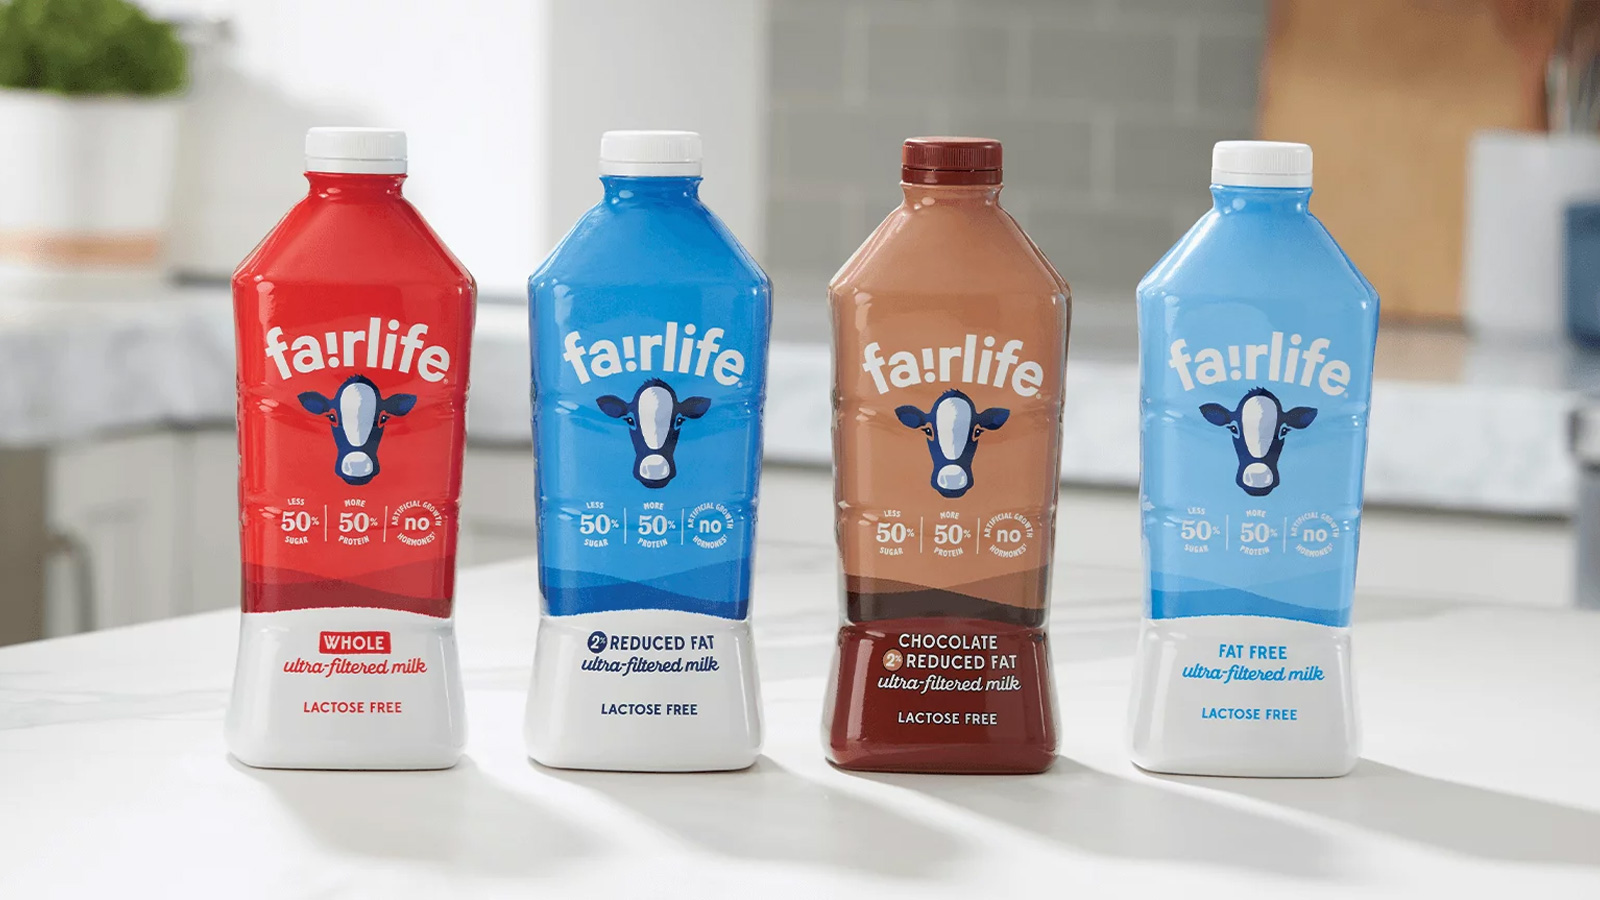
Coca-Cola says Fairlife ransomware attack halts US dairy production
The Coca-Cola Company disclosed today that a ransomware attack impacting its Fairlife dairy subsidiary has disrupted operations, temporarily suspending producti...

Russian hackers trojanize WebEx, Zoom apps to push Starland malware
A financially motivated Russian threat actor tracked as UAT-11795 is using trojanized software to steal credentials and cryptocurrency by deploying a new backdo...
New Spirals ransomware encrypts victim network in under 24 hours
A new ransomware actor called Spirals completed a corporate intrusion, from initial access to data theft and encryption, in less than 24 hours. [...]...
Google Gemini CLI abused as a hacking agent, malware botnet operator
A Russian-speaking threat actor known as "bandcampro" used Google's open-source Gemini CLI AI tool as a hacking agent and to operate a small-scale botnet. [...]...
AsyncAPI npm packages infected with credential-stealing malware
Five malicious versions of AsyncAPI packages were published to the Node Package Manager (npm) in a supply-chain attack that delivered a remote access trojan wit...
AsyncAPI npm packages infected with credential-stealing malware
Five malicious versions of AsyncAPI packages were published to the Node Package Manager (npm) in a supply-chain attack that delivered a remote access trojan wit...

US charges alleged operators of Russian bulletproof hosting service
U.S. federal prosecutors have unsealed charges against three Russian nationals, accusing them of providing bulletproof hosting (BPH) services to ransomware gang...
Nearly 300 GitHub repos pose as legit software to push malware
A threat actor has published hundreds of fake GitHub repositories impersonating legitimate software and security projects to distribute infostealer malware. [.....

Cyberattack at KFC Japan impacting online orders and deliveries
KFC Japan has announced that a cyberattack affecting one of its third-party logistics providers is disrupting food deliveries to restaurants nationwide, raising...
US sanctions VPN, malware providers for enabling ransomware attacks
The U.S. Treasury Department's Office of Foreign Assets Control (OFAC) sanctioned two individuals and one entity for enabling ransomware attacks against U.S. or...
Telegram’s t.me domain suspended at the registry level, breaking links worldwide
Telegram's t.me domain was temporarily placed on serverHold status at the registry level on Tuesday, causing all t.me links to stop resolving through the global...
Japan's largest taxi operator shuts systems after cyberattack
Japan's largest taxi operator, Nihon Kotsu, announced that its systems were compromised in a cyberattack, forcing the company to shut down part of its infrastru...
Hackers backdoor Jscrambler npm package with infostealer malware
The Jscrambler client-side web security company disclosed that a threat actor published a malicious version of its npm package that has been downloaded almost 1...
New CrashStealer malware poses as Apple crash reporting tool
A new macOS information-stealing malware called CrashStealer pretends to be Apple's crash-reporting tool to steal credentials, keychain data, and crypto wallets...
EU sanctions Russian GRU military hackers over cyberattacks
The European Union and the United Kingdom jointly sanctioned dozens of Russian individuals and entities and accused Russia of coordinating a network of hacking ...
RedHook Android malware now uses Wireless ADB for shell access
A new version of the RedHook Android malware abuses the Android Wireless Debugging (Wireless ADB) mechanism in a novel way to gain shell-level privileges withou...
'Ghostcommit' hides prompt injection in images to fool AI agents, steal secrets
A PNG hiding a prompt injection could steal your repo's secrets, researchers demonstrate. The technique, dubbed 'Ghostcommit,' slipped past AI code reviewers Co...
New U-Boot flaws could enable stealthy firmware attacks
Six vulnerabilities in the widely used U-Boot bootloader have been discovered that could allow attackers to execute malicious code during device boot, potential...