Latest IntelligenceMalwarePage 7
Search by keyword →
GitHub ordered to remove decentralized messaging app Bitchat in India
India's Ministry of Home Affairs has ordered GitHub to remove repositories hosting Jack Dorsey's decentralized messaging app Bitchat, arguing that the Bluetooth...
Europol flags 4,340 URLs for removal in 'The Com' crackdown
Europol has flagged 4,340 URLs for removal during a multi-week operation targeting online content linked to "The Com," a loosely organized network of nihilistic...

Tor pauses new feature development to perform privacy audit on Firefox 153
The Tor Project has paused new feature development for Tor Browser 16 as developers work through more than 250 changes inherited from Firefox ESR 153 to ensure ...
New Dolphin X malware uses AI to rank high-value targets
A new Dolphin X remote access trojan claims to use an AI-powered profiling feature to score and rank infected users, helping cybercriminals identify which victi...
Fake Claude app promoted by Bing ads pushes SectopRAT malware
A malvertising campaign on the Bing search service is pushing a fake Claude desktop app installer hosted on a legitimate Claude.ai domain to deliver the SectopR...
macOS flaw lets malware replace trusted apps without security warnings
Security researchers Talal Haj Bakry and Tommy Mysk have disclosed a macOS weakness that allows malware already running under a user's account to silently repla...
Hackers abuse Notepad++ plugins to stealthily install malware
Ukraine's CERT has uncovered attacks distributing an archive containing the legitimate Notepad++ application and a malicious utility called LunchPoke disguised ...
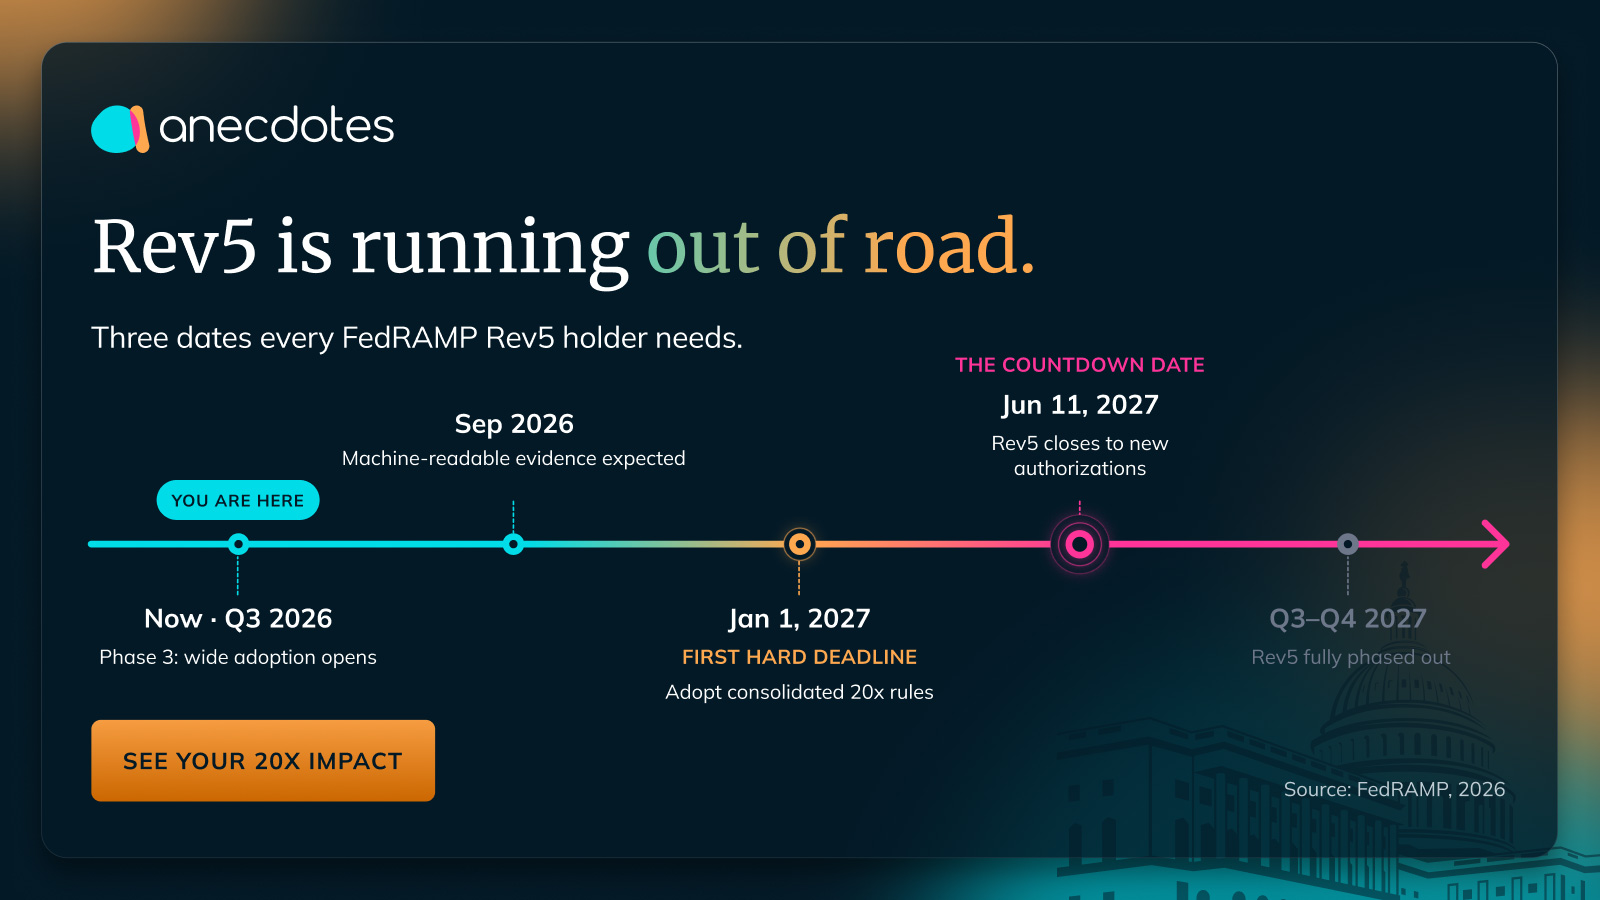
FedRAMP Rev5 Is Ending: What the 20x Transition Really Requires
FedRAMP 20X replaces point-in-time assessments with continuous, machine-readable evidence that demonstrates security controls are working. Anecdotes explains wh...
New Dolphin X infostealer uses AI to identify high-value victims
A newly identified Windows malware called Dolphin X combines information-stealing capabilities with remote access features while targeting credentials from more...
New msaRAT malware uses Chrome, Edge browsers to route C2 traffic
The Chaos ransomware gang is using a new backdoor dubbed msaRAT that hides command-and-control (C2) communication by routing it through the Chrome or Edge brows...
Swiss rail giant Stadler rejects $12.3M ransom demand after cyberattack
Swiss rail vehicle manufacturer Stadler Rail says the Everest ransomware gang demanded about $12.3 million after breaching a data exchange platform shared with ...
How enterprise GenAI can amplify ransomware risk — and how to contain it
Enterprise AI can accelerate ransomware attacks when AI assistants and agents inherit excessive permissions or compromised identities. Acronis explains how iden...
Police dismantle Kratos phishing platform, arrest developer
Authorities in Germany and the U.S. dismantled the central infrastructure of Kratos, a phishing-as-a-service (PhaaS) platform with global reach, and its develop...
FakeGit campaign uses 7,600 GitHub repos to push SmartLoader malware
A large-scale operation dubbed 'FakeGit' is pushing SmartLoader and StealC malware through 7,600 malicious GitHub repositories that accumulated more than 14 mil...
Anubis ransomware claims Coca-Cola Fairlife attack, threatens data leak
The Anubis ransomware gang has claimed responsibility for the cyberattack on Coca-Cola's Fairlife dairy subsidiary, threatening to publish allegedly stolen corp...
Firefox 153 adds built-in Containers for easy account isolation
Mozilla has released Firefox 153, introducing built-in Containers as a native browser feature alongside HDR video playback on Windows, new PDF editing capabilit...
Microsoft shares manual fix for WSUS sync delays and timeouts
Microsoft has shared manual mitigations to help IT administrators fix Windows Server Update Services (WSUS) servers affected by a known issue that causes Window...
JadePuffer agentic attacks now target AI model data with ransomware
The JadePuffer autonomous AI agent has upgraded with custom malware called EncForge that focuses on encrypting AI assets, such as training datasets, vector data...
New HollowGraph malware uses Microsoft Graph for stealthy C2 comms
A malicious component dubbed HollowGraph uses the calendar feature in compromised Microsoft 365 mailboxes as a command-and-control channel to receive attacker c...
An AI SOC Evaluation Guide for Security Leaders
Choosing an AI SOC platform requires understanding how it will perform in your own environment, not just during an evaluation. Prophet Security shares a practic...